All speakers
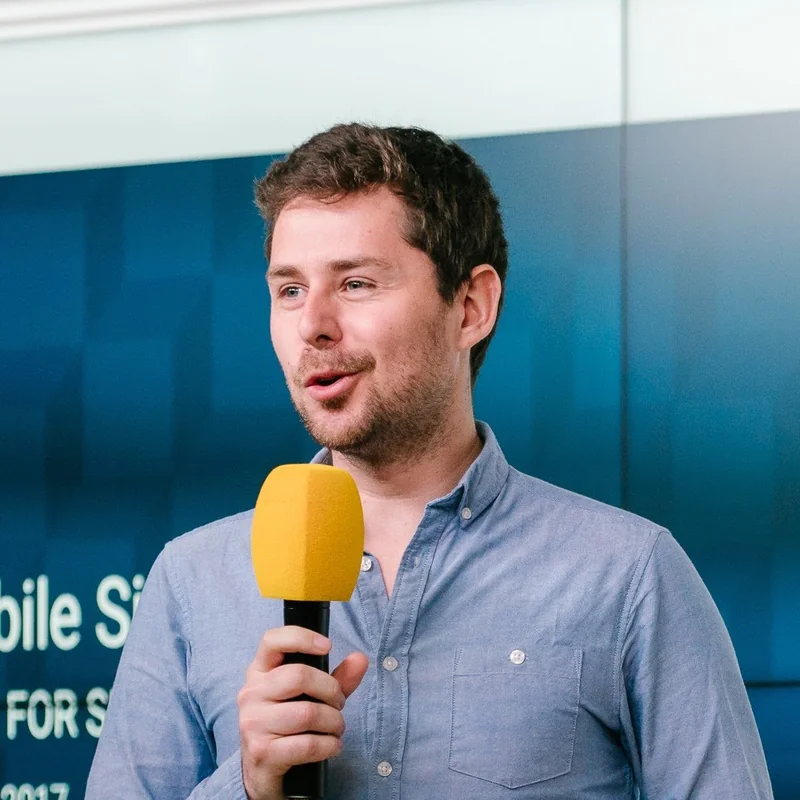
Portrait of Antoine Brossault
Those who implement

Antoine Brossault

Solutions Engineer · Cloudflare

Profile

Background

Antoine Brossault is a Solutions Engineer at Cloudflare, where he works with technical teams and decision-makers on performance, security and AI. He helps them design architectures that hold up in production, from the network and the WAF to Workers and agents.

His career follows one line: making technology understandable and usable. During five and a half years at Google, he first supported large accounts on mobile conversion from Dublin, then on web performance from Paris. He then joined HubSpot as a technical specialist for CRM integrations, before becoming a Senior Sales Engineer at Fastly, where he built proofs of concept around CDN, WAF, DDoS protection and edge compute.

He joined Cloudflare in January 2026. There he works on enterprise AI adoption: application and API security, Zero Trust access, filtering agent and developer traffic, as well as models and agents hosted on the platform. He supports European startups in the F/AI program at Station F.

Antoine is also a regular on technical stages. He has organized and hosted about ten web performance events across Europe, published more than a hundred articles on his blog and built tools such as SpeedChecklist and TheGoodMobileUI. He graduated from MBS School of Business and studied at Universidad de Santiago de Chile.

Perspective

Digital and GenAI credentials

Antoine Brossault sees AI agents at the moment they leave the demo and enter production, with tools, identities and network access. His work at Cloudflare is precisely about securing that transition: blocking a compromised dependency before it reaches a developer laptop, inspecting an agent’s outbound traffic, limiting what it can do with its tokens. That hands-on experience, built on ten years of explaining technical topics to developers and executive committees alike, lets him show real attacks and concrete countermeasures, without needless jargon.
Ecosystem

Their organization

Cloudflare

Solutions Engineer

A global connectivity cloud platform that secures, speeds up and makes applications, APIs and infrastructure reliable, including for artificial intelligence workloads.

Visit Cloudflare

On the program

Their session

15:20 · Loire Room

40 min · Talk

“My AI agents are the new target for attackers”

By 2026, everyone has an agent. Almost nobody has governance. At Cloudflare, the whole company was equipped in under a year, and merge velocity doubled. What made the difference was not the model we picked. It was the architecture around it. This talk explains why we built our own AI stack, and the decisions that followed: centralizing every model call behind a single gateway, moving security to the network layer instead of into each tool, governing access to internal data by identity, and running agent-generated code in an isolated environment. We’ll talk architecture, results and terminal, and we’ll stand behind one opinion: the harness and the model are two separate things. We’ll cover: - running generated code in sandboxed environments, with outbound access filtering; - controlling data access through identity and least privilege; - protecting against leaks of secrets and sensitive data; - centralizing model calls, with no API keys on user machines; - preventing generated applications from being exposed publicly by accident. We’ll illustrate this with Cloudflare OS, our open source harness, and in particular its Gatekeepers mechanism. They provide stronger security than a classic MCP integration: each agent or application gets only the capabilities it strictly needs, actions are logged, and sensitive operations can require human approval. The project and the details of this architecture: - Cloudflare OS - How the Gatekeepers work - The sandbox and access control model

  • AI agents
  • Governance
  • Agent security
  • Cloudflare OS